From Compromised Membership Product to Controlled Access Platform
System Architecture //
1. Project Overview
This was a live membership product with a website, payments, CRM, Telegram access and several historical automations. When I joined, the system showed signs of compromise: legacy PHP code, backdoor behaviour, SEO spam, unclear access boundaries and payment logic that was unsafe to carry into a new release
I was brought in to restore control of the product and relaunch it without carrying the old infected environment forward
2. The Challenge
3. Solution and Delivery
Clean environment instead of blind migration
I inventoried domains, servers, databases, integrations and legacy dependencies, created a full backup of files, database and logs, and verified restoration in an isolated environment. The new deployment was built separately; old code, keys and unknown integrations were not carried forward automatically
Controlled website and payment path
The mobile-first website, plan logic, registration form and payment path were rebuilt. Server-side validation now checks the payment signature, merchant, order ID, amount, currency and status, while duplicate callbacks cannot grant access twice
Access as a business entity
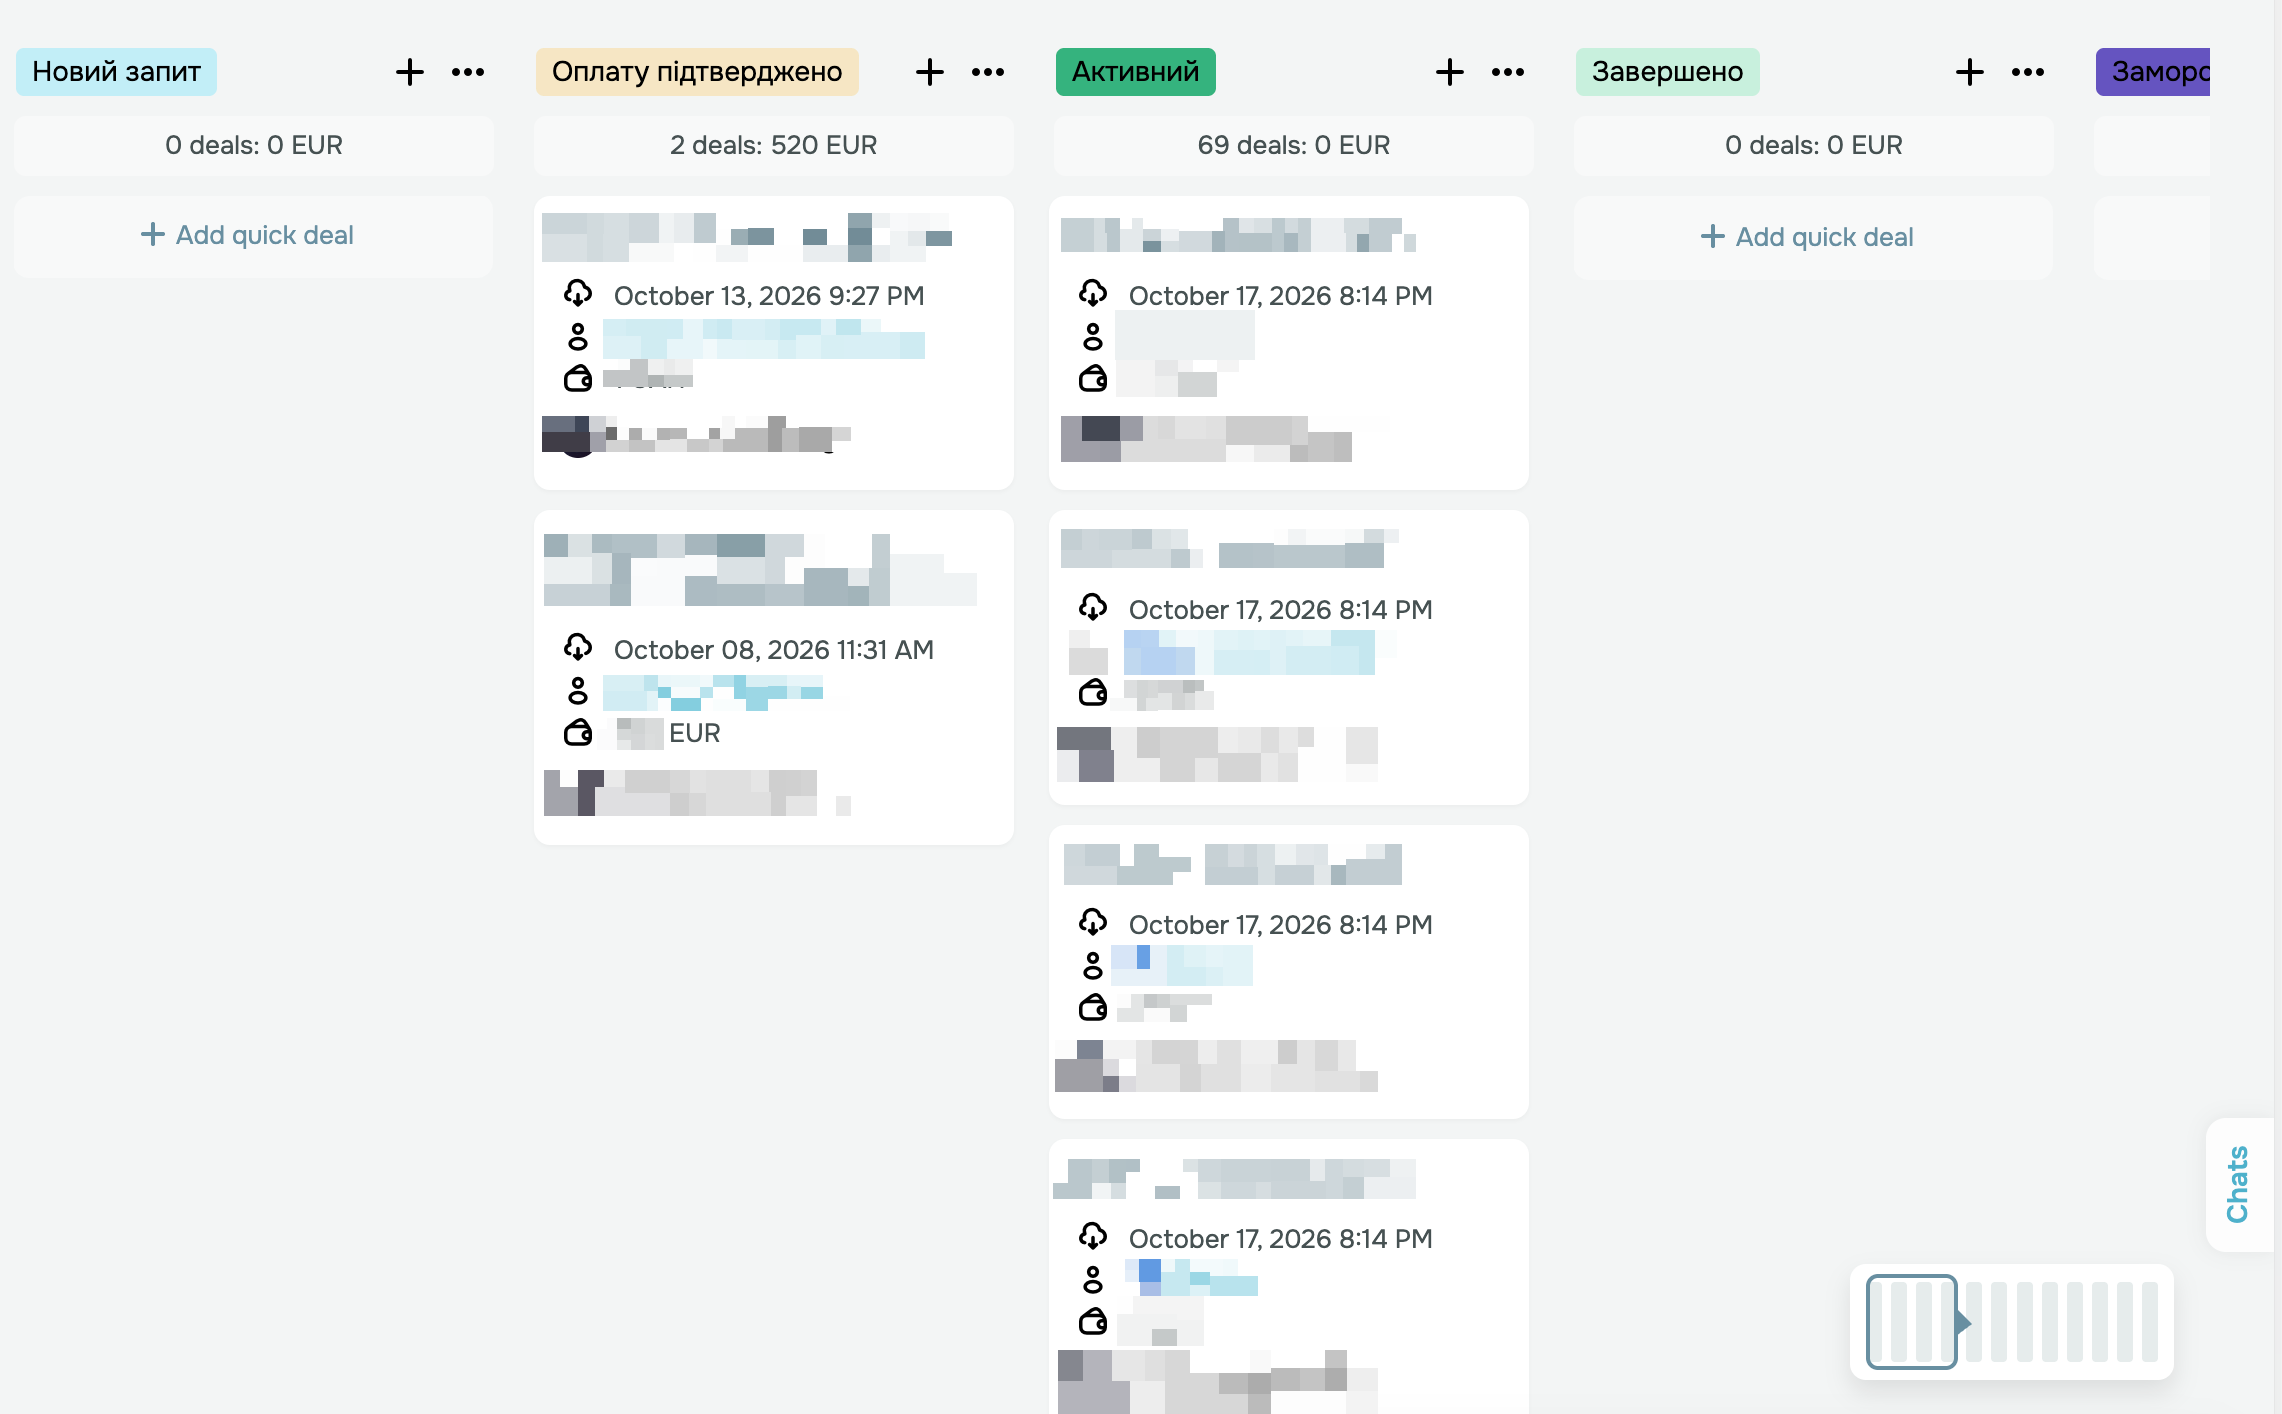
A payment no longer triggers a blind chain of disconnected commands. The system connects the contact, entitlement, term, renewal, freeze and actual Telegram ID, checks the entitlement before membership approval and keeps manual exceptions separate from payment records
Verification before reopening sales
I ran 16 test suites covering duplicate callbacks, expired entitlements, unknown profiles, existing members, join requests, manual grants and rejection paths. A real small payment, CRM record and access behaviour were also checked in an isolated test flow
4. Result
5. Technical Outcome
Instead of a system where compromise could only be suspected, the product now has a clean deployment boundary, reproducible access rules, idempotent payment handling, manual review for exceptions and a verified recovery path
This was not just a security fix or a new website. I restored control after an attack, preserved working member entitlements and reopened sales only after the critical paths could be tested and explained